Whitesec One · Essential Eight
Essential Eight maturity, strategy by strategy.
Assess the eight mitigation strategies against the Australian Signals Directorate’s November 2023 maturity model, requirement by requirement. See the level each strategy truly reaches, then work the gaps through remediation, patch windows and recurring checks.
Screenshot of the live dashboard with sample data.
- Model
- ASD Essential Eight Maturity Model, November 2023
- Rule
- A level counts only when it and every level below are fully met
- Overall level
- The lowest across the eight strategies, never an average
- Outcome
- Assessed maturity per strategy, against your target
Where the Essential Eight stands
ASD Essentials is replacing it. Here is what that means for your evidence.
On 15 October 2026 the Australian Signals Directorate launched ASD Essentials, a principles-based framework that will replace the Essential Eight. Maturity levels are replaced by effectiveness ratings, and existing ratings do not convert.
ASD has said it does not recommend slowing or stopping existing uplift programs, and both frameworks remain published during the transition. The Whitesec One workspace assesses against the November 2023 maturity model today. Whitesec AU maps Essential Eight work to ASD Essentials as a consulting service, and the requirement-level evidence you keep stays useful as the input to that mapping.
What the workspace does today
From a scope statement to a working remediation plan.
Each part is recorded against a named version of the ASD criteria, so an assessment can be explained months later.
Scope and targets
A scope statement in the ASD's wording, an organisation target from Level One to Level Three with a date and justification, and a target per strategy that needs its own justification when it differs.
Requirement-level assessments
Each requirement is recorded as effective, alternate control, ineffective, no visibility, not implemented or not applicable, with evidence quality and test method, against a named version of the criteria.
Maturity that cannot be rounded up
A level is met only when every requirement at it is effective or covered by an alternate control. Multi-factor authentication, administrative privileges, application control and user application hardening are held at Level One until an incident response plan is linked.
From gap to remediation
Requirements not yet met are prioritised by the size of the gap and turned into remediation actions with owners and dates, which can raise corrective actions on the shared ISO 27001 register.
Patch windows from the release date
Each window is worked out from the date the fix was released: 48 hours, two weeks or one month, depending on the asset, the severity and your target level. Accepting the risk on a patch needs a second person.
Evidence and recurring checks
Evidence by strategy with expiry tracking, a compliance calendar for recurring patching, scans, reviews, tests, backup verification and access reviews, and five exportable reports.
- app.whitesec.one/essential8/dashboard
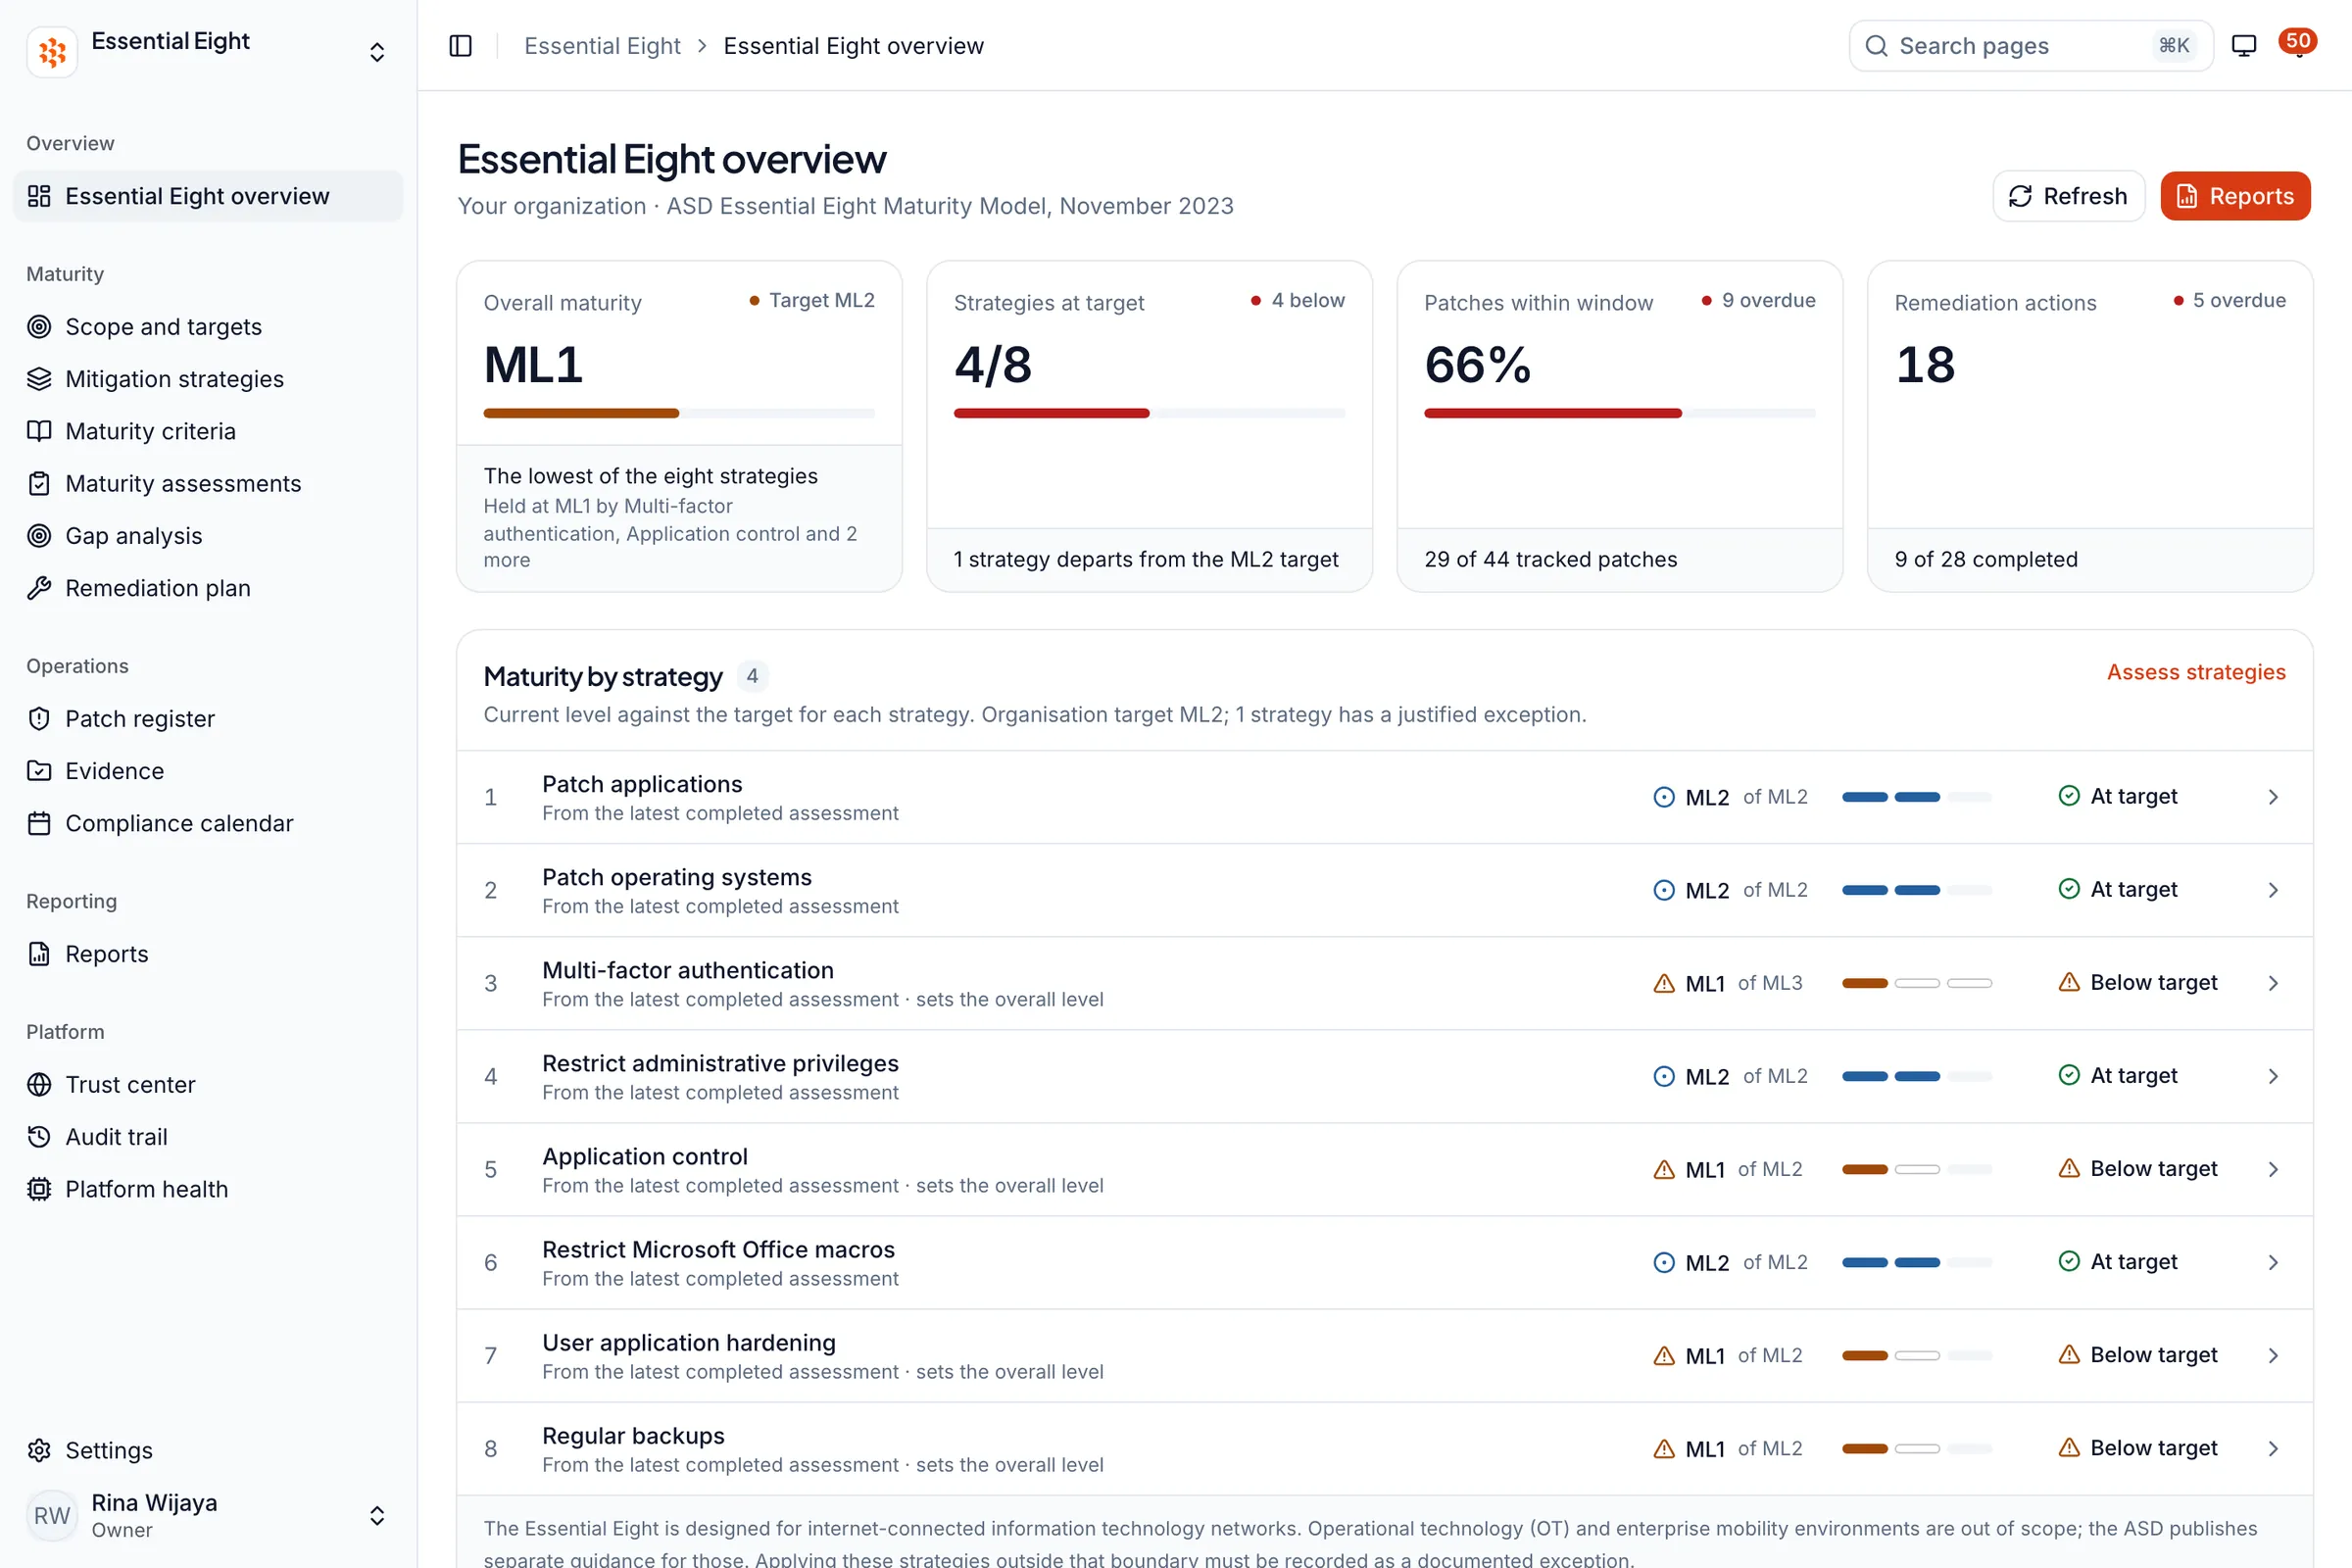
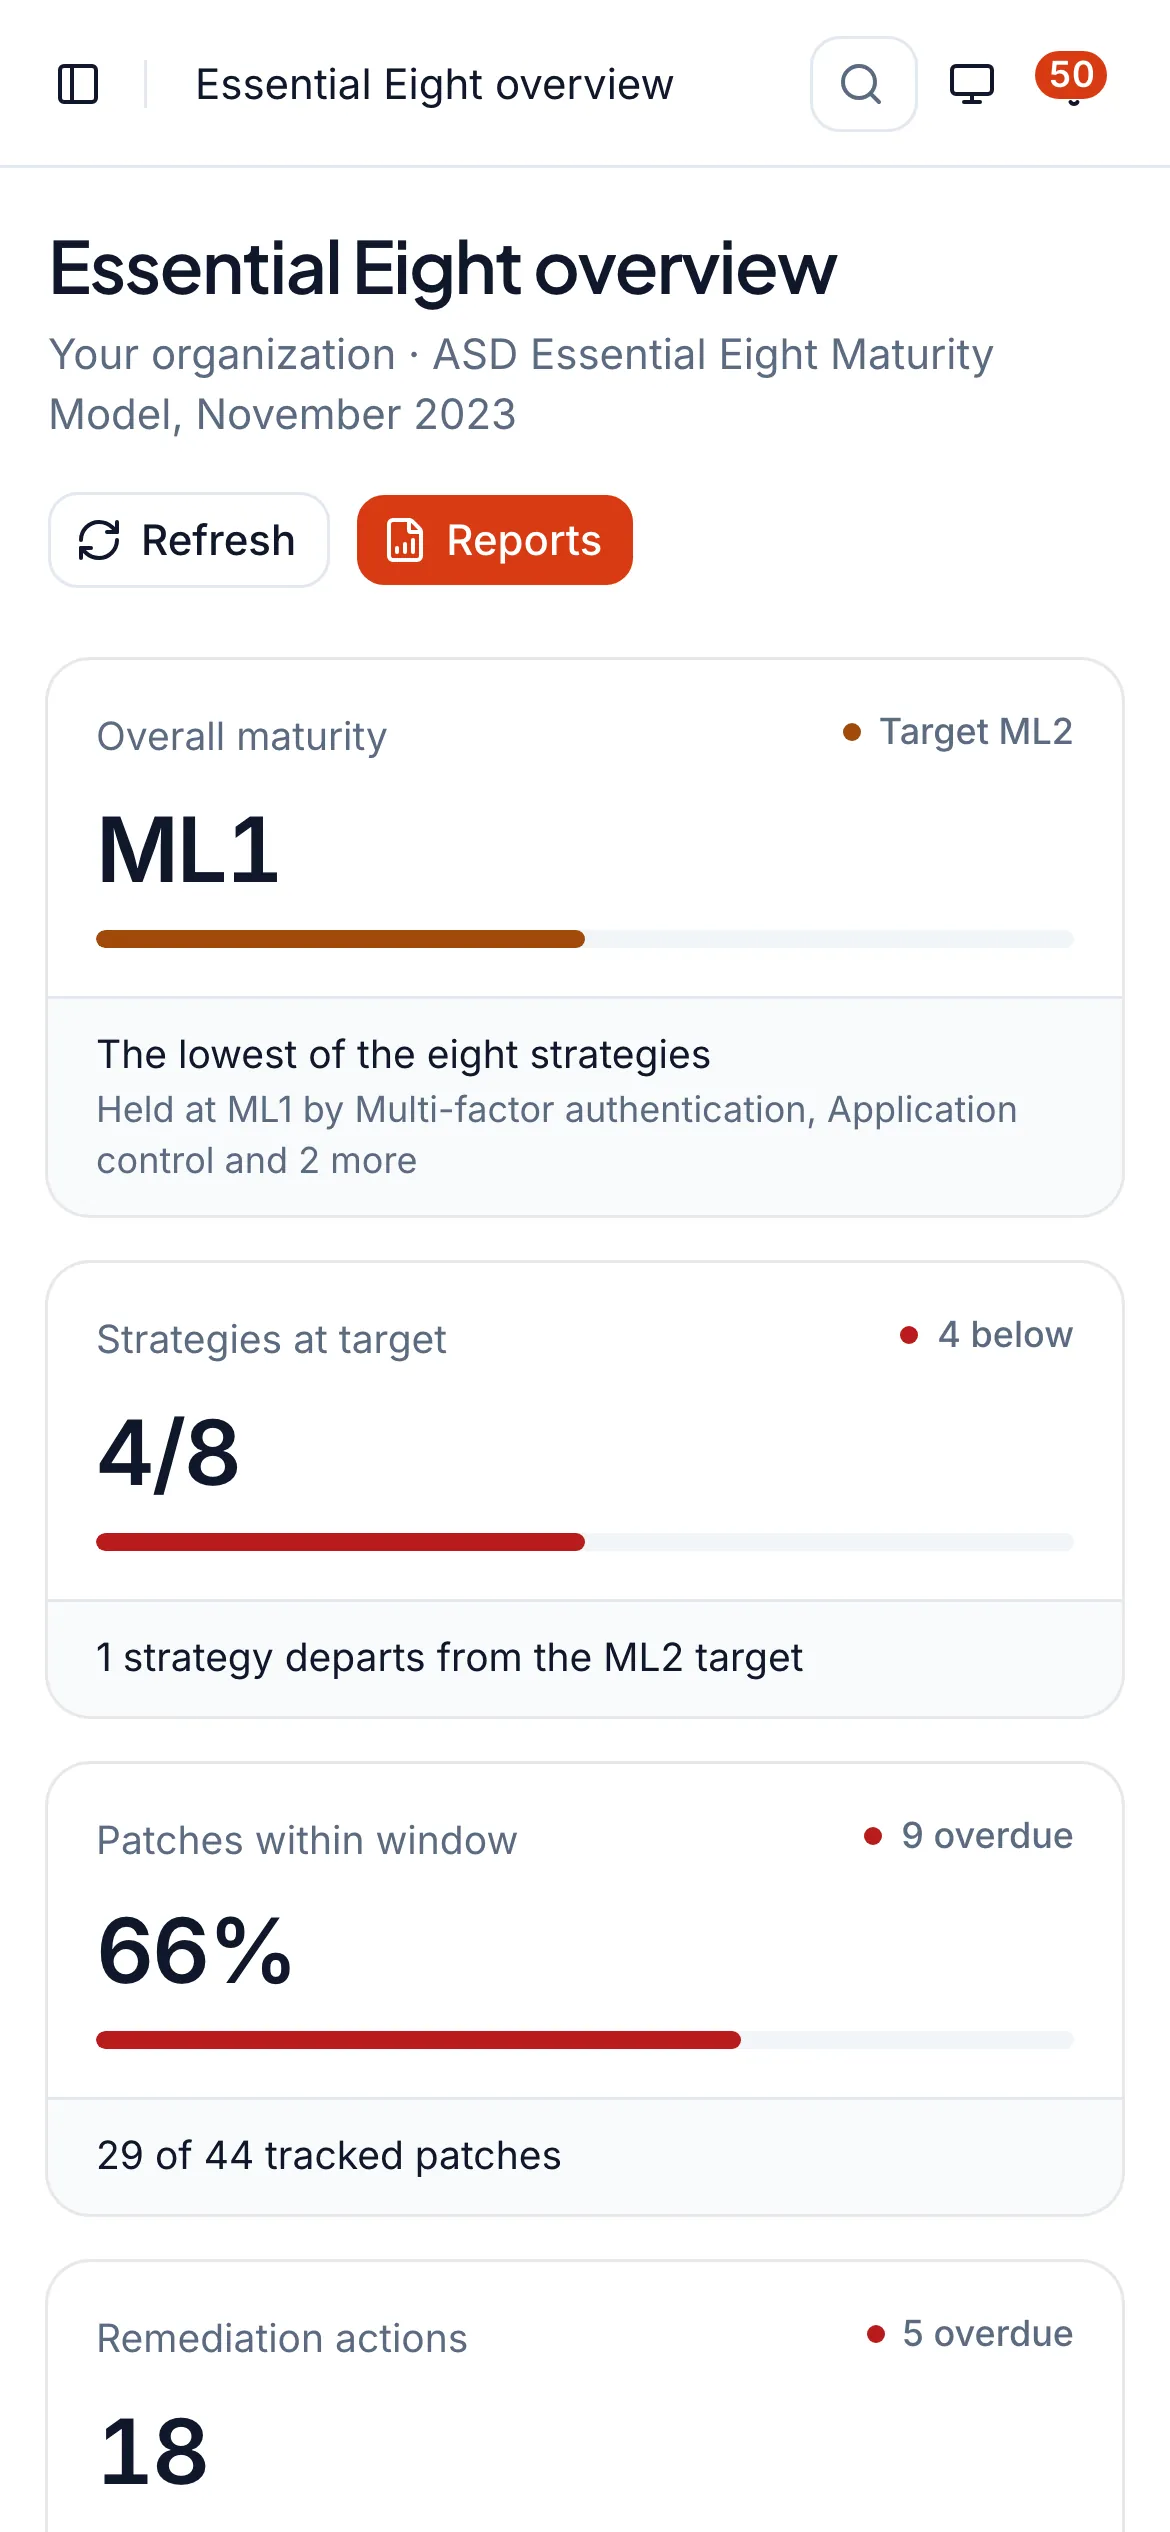
Essential Eight overview
Maturity by strategy against the ASD November 2023 model. The overall level is the lowest, never an average.
- app.whitesec.one/essential8/strategies
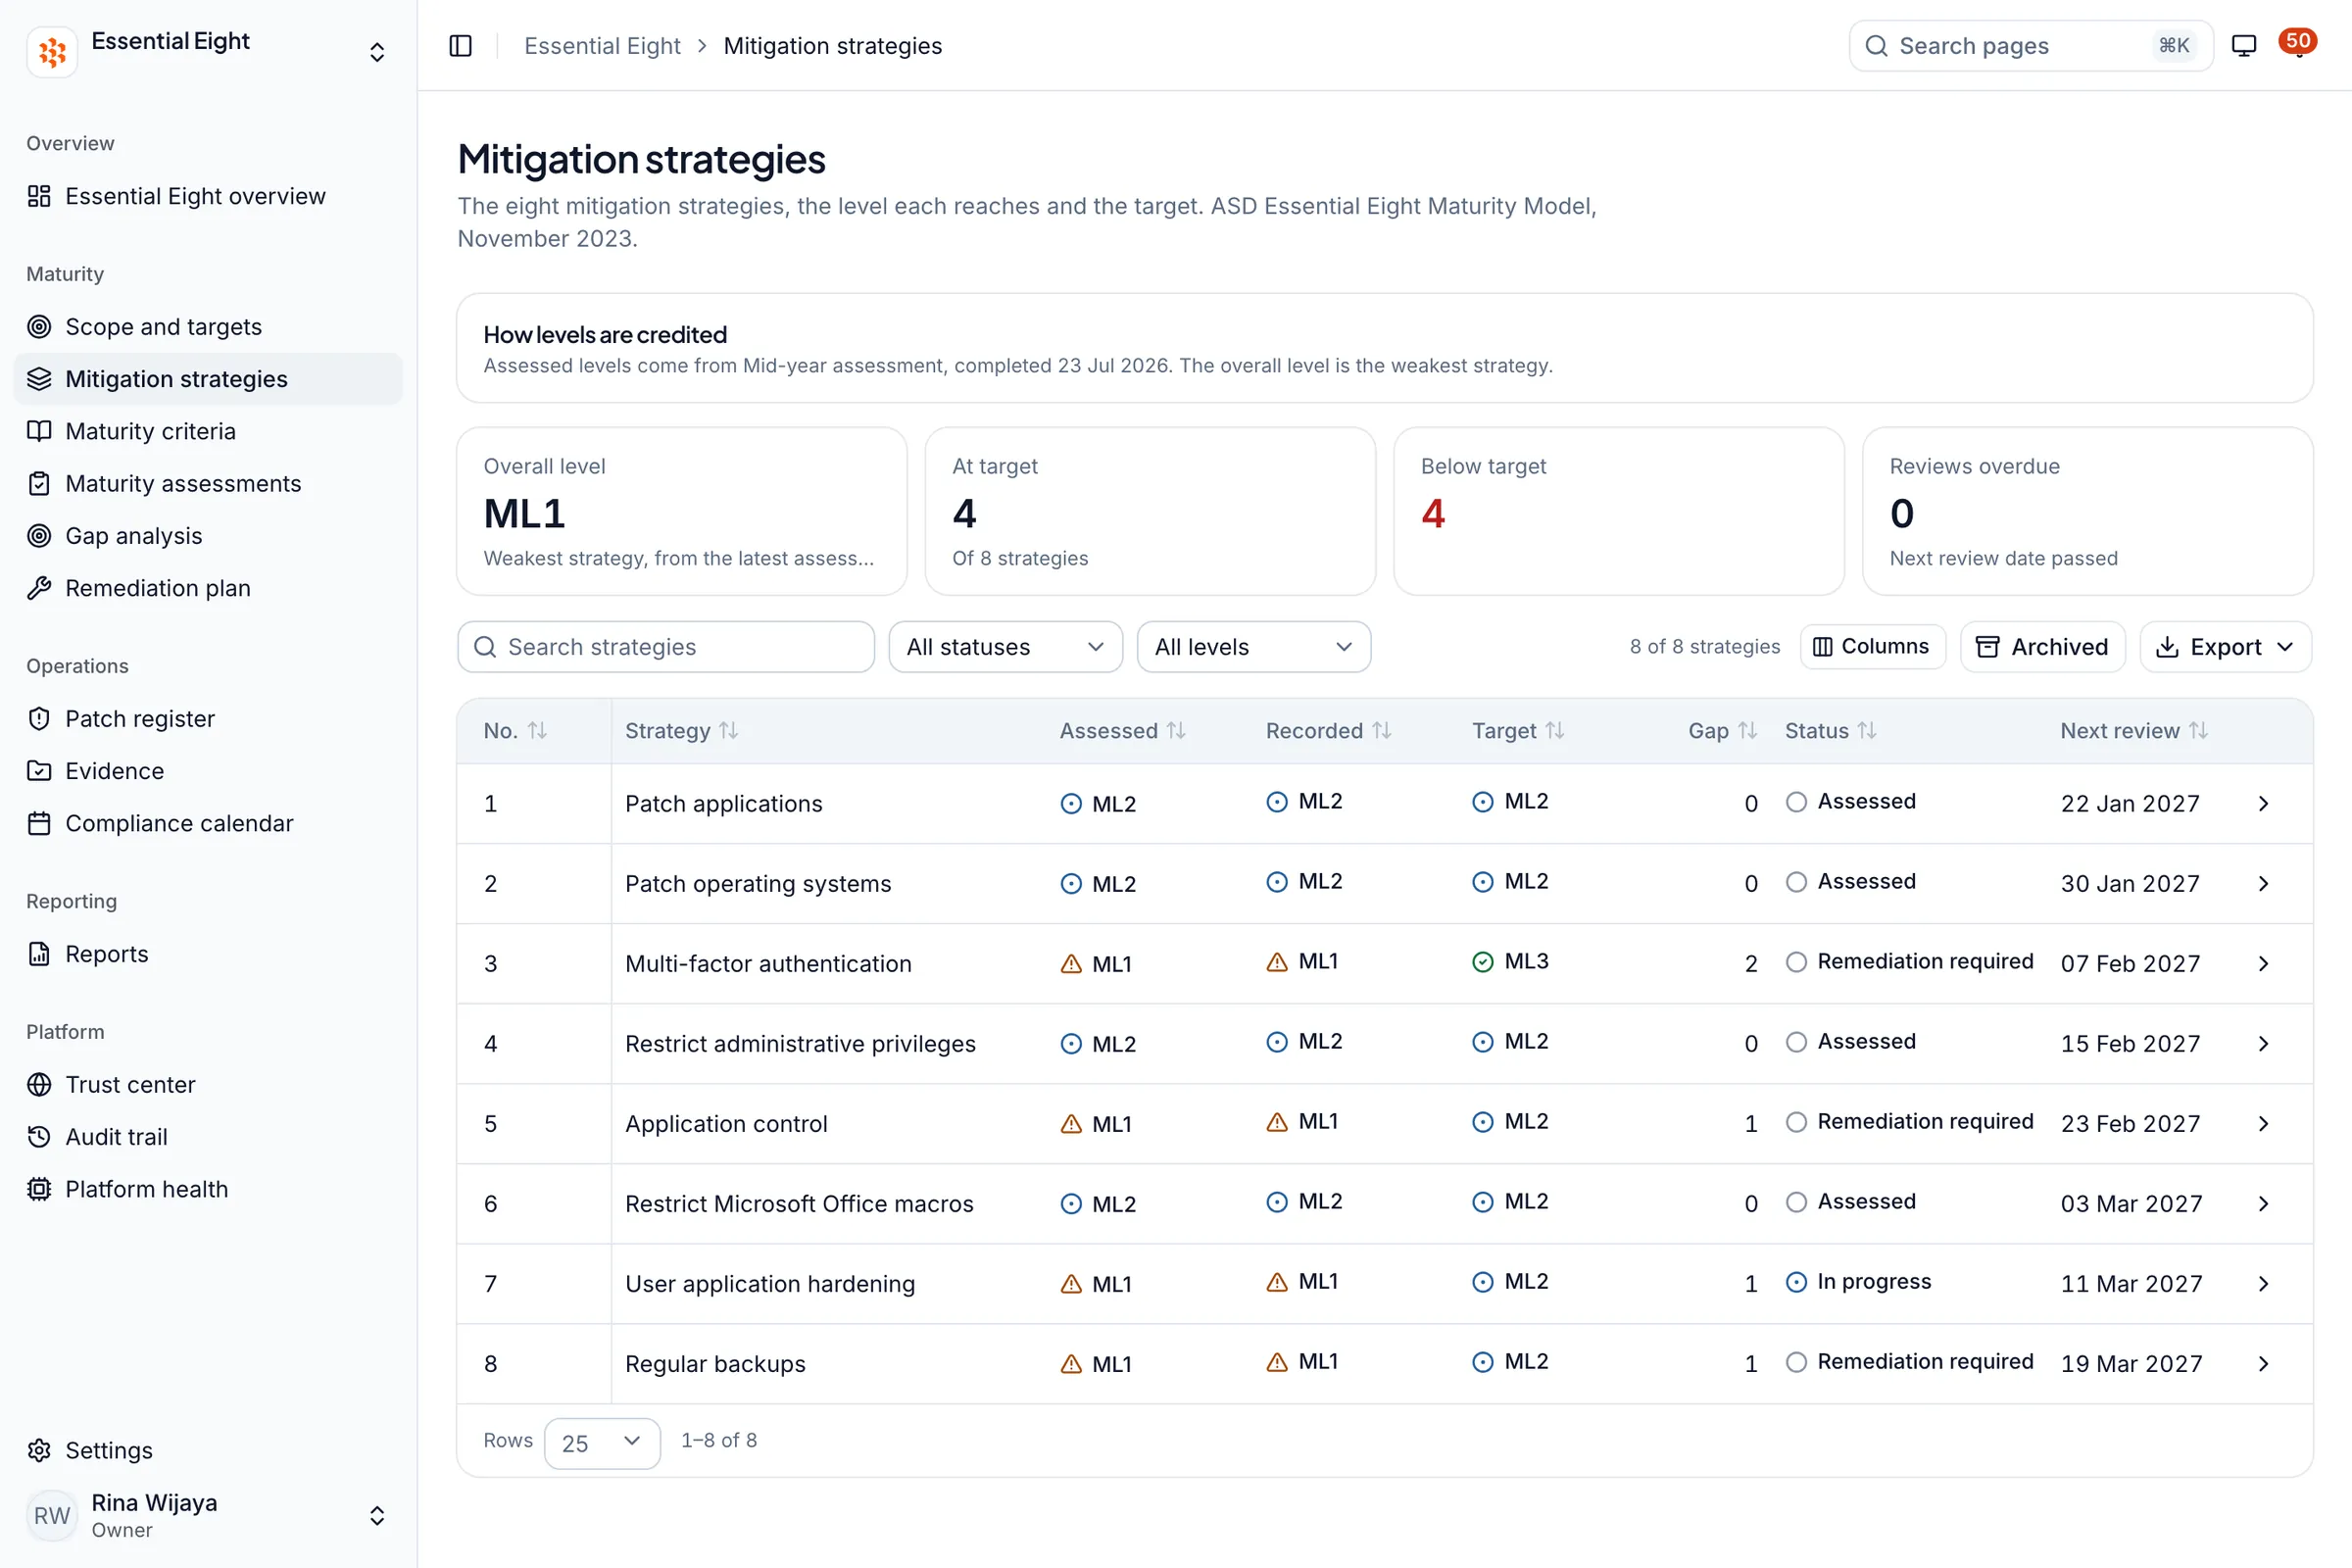
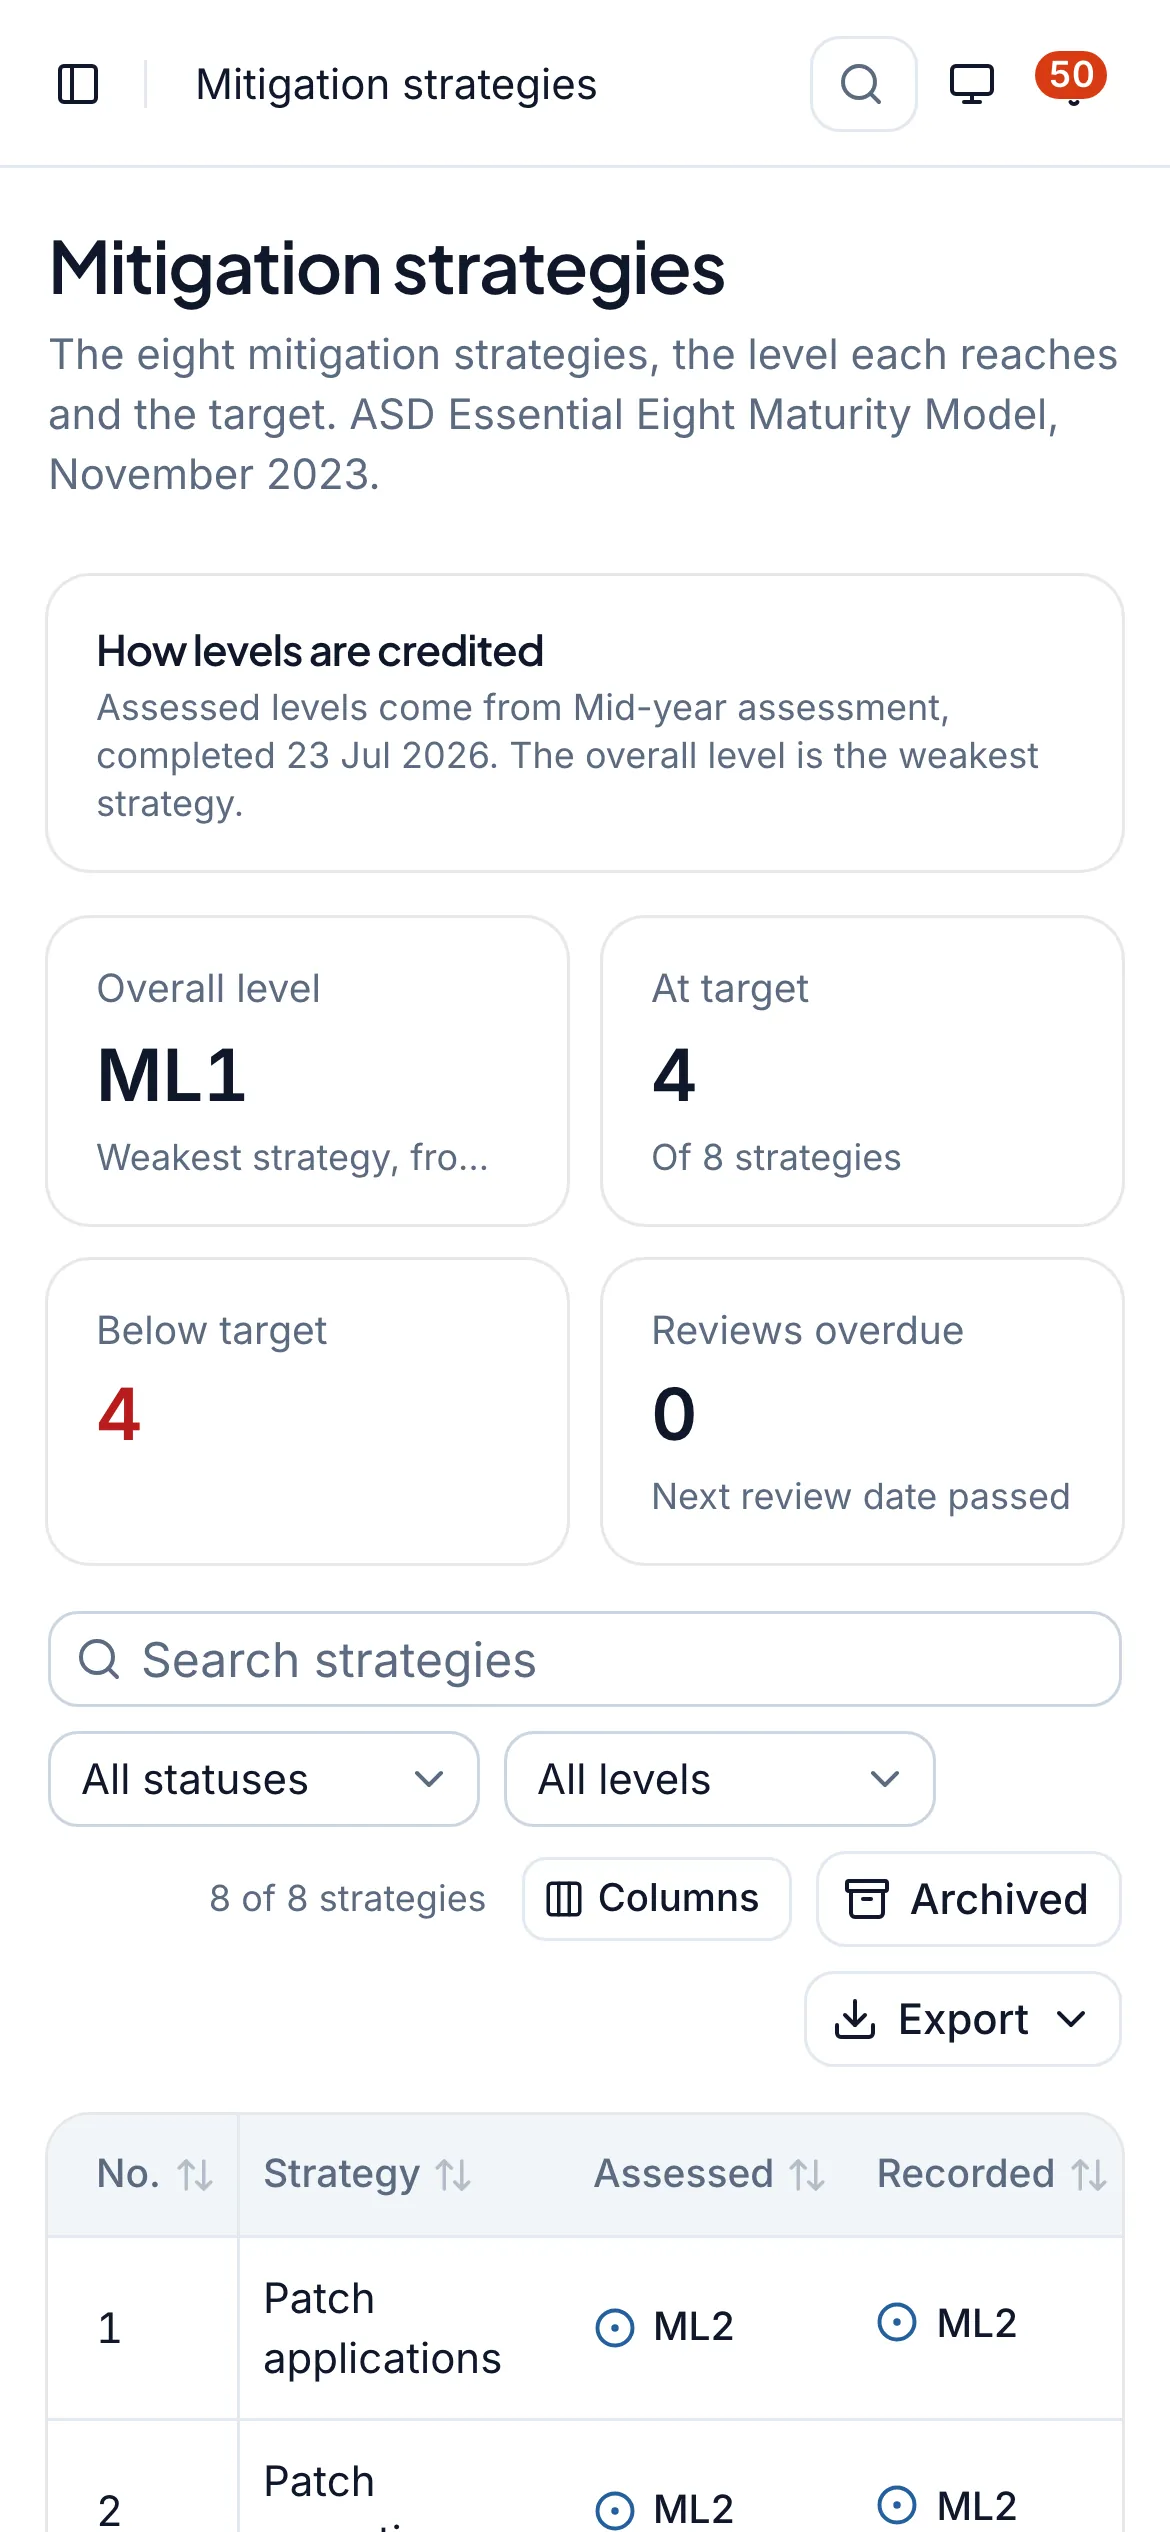
Mitigation strategies
The eight strategies with assessed level, target, gap and next review.
Screenshot of the live dashboard with sample data.
The eight strategies
Each one assessed on its own, and the weakest sets the level.
Level Zero is weaknesses, Level One opportunistic, Level Two targeted and Level Three adaptive. Each level is built to withstand a more capable adversary.
- 01
Patch applications
Apply security updates to applications and drivers within set timeframes, and remove applications that are no longer supported.
- 02
Patch operating systems
Apply security updates to operating systems and firmware within set timeframes, and replace versions that are no longer supported.
- 03
Multi-factor authentication
Require stronger sign-in for users and administrators of online services and important data repositories.
- 04
Restrict administrative privileges
Validate, limit and review privileged access, and keep privileged accounts away from email and web browsing.
- 05
Application control
Allow only approved programs, scripts and libraries to run on workstations and servers.
- 06
Restrict Microsoft Office macros
Block macros from the internet and allow only trusted, vetted macros to run.
- 07
User application hardening
Harden web browsers, office and PDF software, and turn off features that are not needed.
- 08
Regular backups
Back up important data, software and configuration settings, and test that they can be restored.
With Whitesec AU
Assessment in the platform, judgement from the consultants.
The workspace records the assessment. Whitesec AU brings the technical verification and the plan to close the gaps.
Essential Eight Pilot
A rapid gap analysis and tender-readiness scorecard against the maturity levels.
Continuous GRC and Telemetry
Ongoing technical monitoring between audits, a separate service from the workspace.
Whitesec One overview
ISO 27001, SOC 2 and the shared registers behind every framework.
Questions
Essential Eight in Whitesec One
See your Essential Eight position, requirement by requirement.
We walk through the workspace with the team in West Perth and agree how it fits your target and your next tender or renewal.